
Singahi Publishes Free ISO 27001:2022 Guide Covering All 93 Annex A Controls
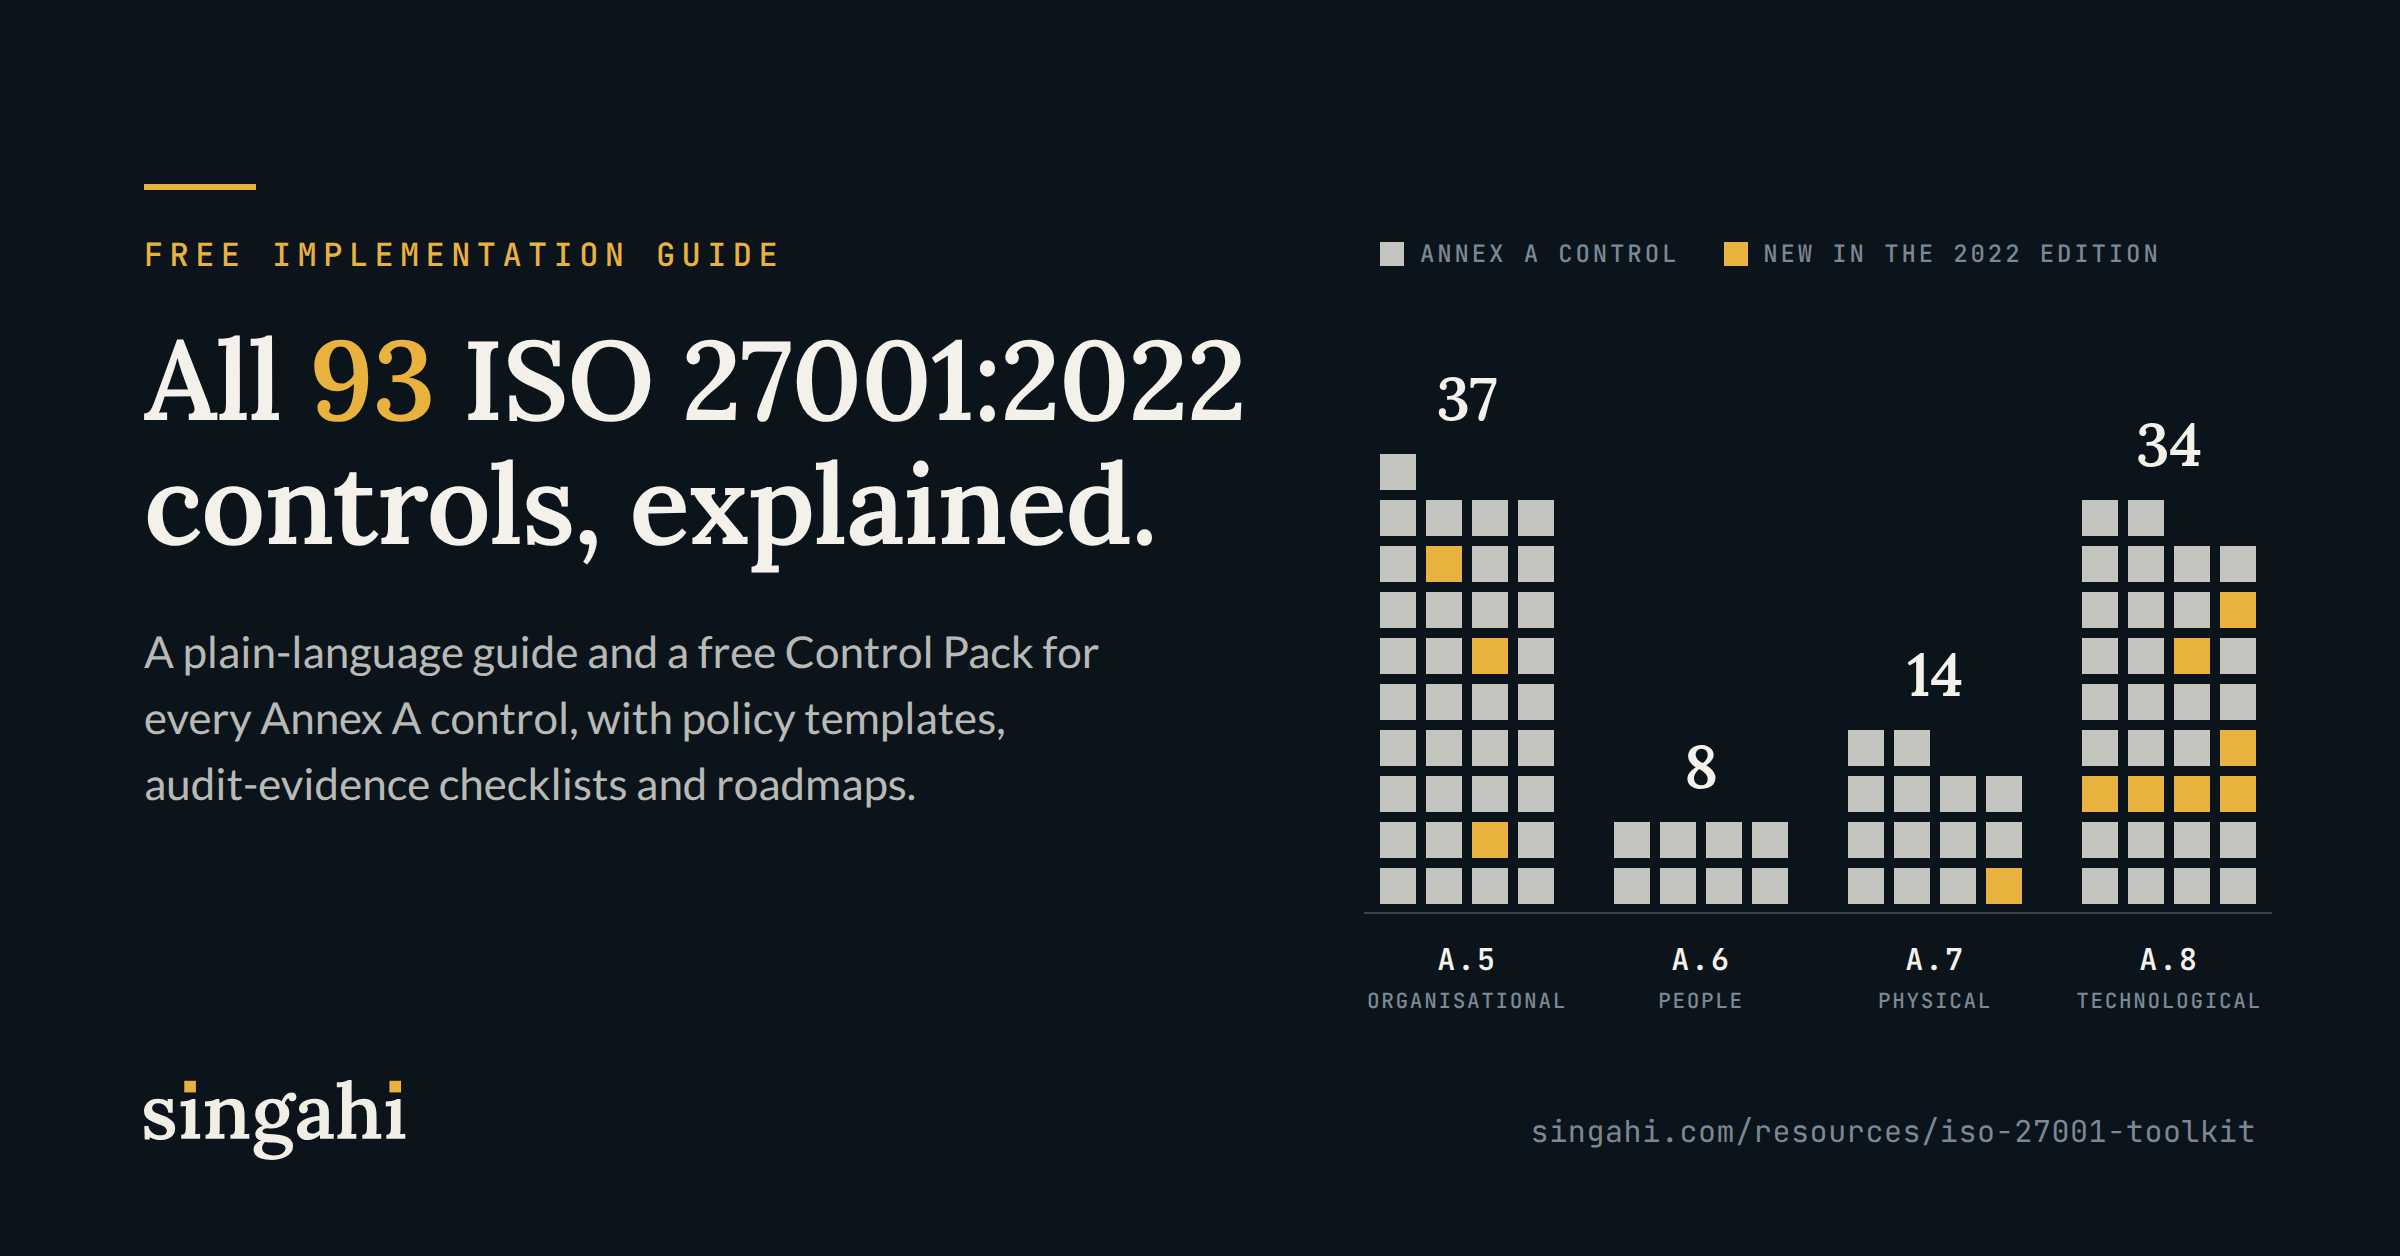
Singahi's free ISO 27001:2022 implementation guide covers all 93 Annex A controls across four themes: 37 organisational, 8 people, 14 physical and 34 technological, including the 11 controls new in the 2022 edition.
The free guide takes growing companies through ISO 27001:2022 one control at a time. Guides to ISO 22301, ISO/IEC 27701 and ISO/IEC 42001 will follow.
LUCKNOW, UTTAR PRADESH, INDIA, October 1, 2026 /EINPresswire.com/ -- Singahi, a cybersecurity and compliance firm, today announced the completion of its free implementation guide to ISO/IEC 27001:2022, which now covers all 93 Annex A controls. The firm began publishing the guide on 1 July 2026, adding one control a day, and the final instalment went live on 1 October. Guides to ISO 22301, ISO/IEC 27701 and ISO/IEC 42001 will follow over the coming months.
ISO 27001 certification is now a common requirement in enterprise procurement and investor due diligence. The transition period for the 2022 edition ended on 31 October 2025, and certificates issued against ISO 27001:2013 are no longer valid, so any organisation certifying or renewing today must work to the revised Annex A. The revision restructures the previous 114 controls into 93, grouped under four themes (organisational, people, physical and technological), and introduces 11 new controls in areas such as threat intelligence, cloud services, data leakage prevention, data masking and secure coding.
For most companies, applying the standard is where the real work lies. Teams have to decide which controls are relevant, turn each one into policy and day-to-day practice, and then produce the evidence an auditor will ask for. One common misunderstanding, according to Singahi, is that every Annex A control is mandatory. In practice, organisations determine the controls they need through risk assessment and treatment, check them against Annex A, and record each decision, with its justification, in a Statement of Applicability.
"In most of the readiness reviews we carry out, the technology is in reasonable shape. What trips companies up is the documentation, because day-to-day practice often hasn't been written down in a way an auditor can follow," said a spokesperson for Singahi. "We wrote the guide so that whoever is leading the certification effort can open any control, see what the auditor will look for, and start from a working draft rather than a blank page."
Each control has its own plain-language article covering what the requirement means, how organisations typically implement it and the questions auditors commonly raise. Where relevant, the articles also address Indian regulatory requirements such as the Digital Personal Data Protection (DPDP) Act, 2023, as well as RBI and SEBI guidance. Alongside every article is a downloadable Control Pack of templates and working documents. A typical pack includes:
- a policy template and supporting procedure
- implementation and audit-evidence checklists
- a risk register, KPIs and a gap analysis
- a RACI matrix and an implementation roadmap
The articles are open to read without registration, and the Control Packs are free to download after a short sign-up.
For organisations starting out, Singahi recommends agreeing the scope of the information security management system first and completing the risk assessment before writing any policies. The gap analysis in each Control Pack can then show where existing practice already meets the requirement and where work is needed. Evidence collection should start early. Certification auditors look for proof that controls have been operating for some time, not documents produced in the weeks before the audit. They will also expect to see that an internal audit and a management review have taken place.
Three further guides will follow in the same format. The first, on ISO 22301 for business continuity management, starts on 2 October 2026 and will run to 26 articles covering the standard clause by clause, including business impact analysis, continuity strategies, business continuity plans and exercise programmes. The series maps to ISO 27001 where the two standards overlap.
The second, expected from late October, will cover ISO/IEC 27701 for privacy information management. It will follow the 2025 edition of the standard, which can now be adopted on its own rather than only as an extension to ISO 27001. Singahi expects it to be of particular interest to Indian organisations preparing for the DPDP Rules, 2025, most of whose obligations take effect in May 2027.
The third, expected from December 2026, will cover ISO/IEC 42001, the international standard for AI management systems. Published in December 2023, it applies to organisations that develop, provide or use AI-based products and services and need to show that those systems are governed responsibly.
Organisations that want hands-on support can engage Singahi for gap assessments, internal audits and implementation work ahead of certification.
Availability
The ISO 27001:2022 guide is available now at singahi.com/resources/iso-27001-toolkit.
About Singahi
Singahi is a cybersecurity and compliance firm that helps growing companies prove their security to customers, investors and regulators. It works as one team for compliance, testing and managed security, so clients can start with a single service and add others as their needs grow. The team holds certifications including OSCP, CISSP, CISA, CEH and ISO 27001 Lead Auditor. Headquartered in Lucknow, India, Singahi serves clients in the USA, Canada, the UK, Germany, India and the Middle East. For more information, visit singahi.com.
Media Relations
SINGAHI TECHNOLOGIES PRIVATE LIMITED
+91 9580230300
sales@singahi.com
Visit us on social media:
LinkedIn
Facebook
YouTube
X
Free ISO 27001:2022 Implementation Guide: All 93 Annex A Controls | Singahi
Legal Disclaimer:
EIN Presswire provides this news content "as is" without warranty of any kind. We do not accept any responsibility or liability for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this article. If you have any complaints or copyright issues related to this article, kindly contact the author above.
